The Software Supply Chain Security Platform
Delivering visibility into software supply chain risks, starting with the most comprehensive SBOM.
Reduce Software Supply Chain Risk End-to-End
Protect your software supply chain end-to-end. Devs can ensure that open-source components, CI/CD workflows, and release pipelines are safe. Plus, the SOC gets greater visibility of the entire build process, bolstering your organization's last line of defense.
Platform & Products
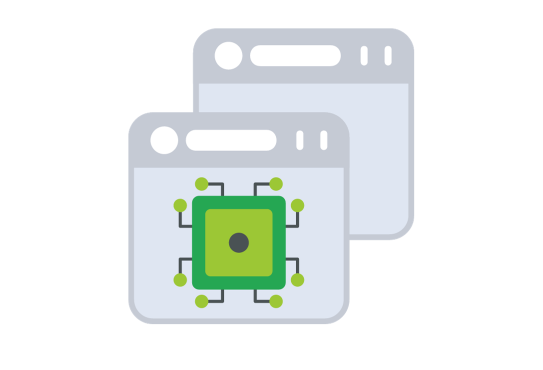
ANY FILE. ANY LOCATION. ANY THREAT.
Titanium Platform
A machine learning hybrid cloud platform that analyzes thousands of file types at scale and monitors a vast index of goodware and malware for future threats.

ReversingLabs Software Supply Chain Security (SSCS)
Protects CI/CD workflows, containers, and release packages so DevSecOps teams can release software with confidence.
ReversingLabs Threat Intelligence
Titaniumcloud
A threat intelligence service delivering file reputation, threat classification, and rich context on tens of billions of files through REST APIs and feeds.
ReversingLabs Cloud Deep Scan
Continuously scans Amazon Web Services S3 buckets for threats and classifies files up to 10GB so teams can prioritize malicious files.
ReversingLabs Elastic Threat Infrastructure
Titaniumscale
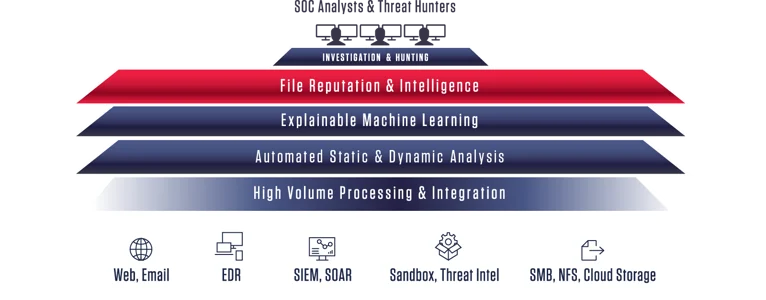
Assesses millions of files from web traffic, email, endpoints, and storage, then feeds enriched results into SIEM, SOAR, and analytics platforms.
ReversingLabs Threat Analysis & Hunting
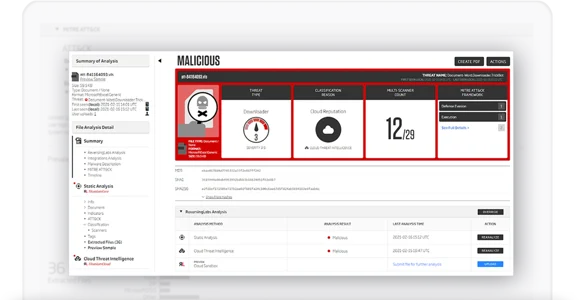
A1000
Advanced hunting and investigation built on the TitaniumCore static analysis engine, with file reputation, YARA rule matching, and sandbox integration.

Open-Source YARA Rules
Open-source YARA rules built for zero false positives and tested against a cloud repository of 25B unique binaries before release on GitHub.
Protect Against Software Supply Chain Attacks
A unified software supply chain security platform that lets Dev and SOC teams release software and respond to incidents with speed and confidence.
SBOMs: Your Software
Ingredient List
Knowing what is in your software is the first step in securing it. Get your free Software Bill of Materials (SBOM) report.
Verify Third Party Software
Automates security assessments, policy control, and component visibility so Third-Party Risk Management, Procurement, and IT teams can safely accept third-party software and updates.
Verify Software Build & Release
Assesses components, releases, and containers for malware and tampering so teams can release software that keeps customer trust.
Triage Alerts Faster
Delivers the right data in the right place to accelerate and prioritize alert triage for stretched SOC teams.
Automate Incident Response
Removes manual research and reverse engineering, surfacing local threat context in real time inside your incident response or SOAR system.
Expand SIEM and SOAR Visibility
Automated static analysis of incoming files enriches any SIEM or SOAR with malware correlation and faster incident response.
Protect Cloud File Sharing
Scans cloud file sharing and synchronization systems for malware and suspicious content to isolate threats before they spread.
Detect and Prevent Ransomware
Before It Strikes
Detect emergent ransomware attacks early to prevent data loss and business interruption.
Advance Your Malware Lab
A centralized malware analysis service gives the digital business a single point of contact for escalated workflows.
Hunt Threats Continuously
Continuous 24x7 threat hunting needs tooling that replaces manual research.
Optimize Sandbox Performance
Static analysis unpacks inbound files without executing them, so sandboxes process only the critical files, faster.
Prevent Phishing and Zero-Day Email Attacks
Integrates with email platforms, gateways, and SMTP relay points for real-time analysis of all email content and inbound traffic.
Expose All Hidden
Malware in EDRs
Integrates with EDR solutions to identify malicious files without execution.
Fuel Threat Intelligence
Platforms
APIs and feeds connect actionable malware indicators to threat intelligence platforms and existing workflows.
ReversingLabs Threat Intelligence for Microsoft Sentinel
Enhances Microsoft Sentinel with ReversingLabs threat intelligence. Start a free trial.
The Power of Complex Binary Analysis
Delivering visibility into software supply chain risks, starting with the most comprehensive SBOM.
Solutions Offered
Explore our wide range of cutting-edge technologies.