
Agentic AI Orchestration Layer
The AI-native cockpit
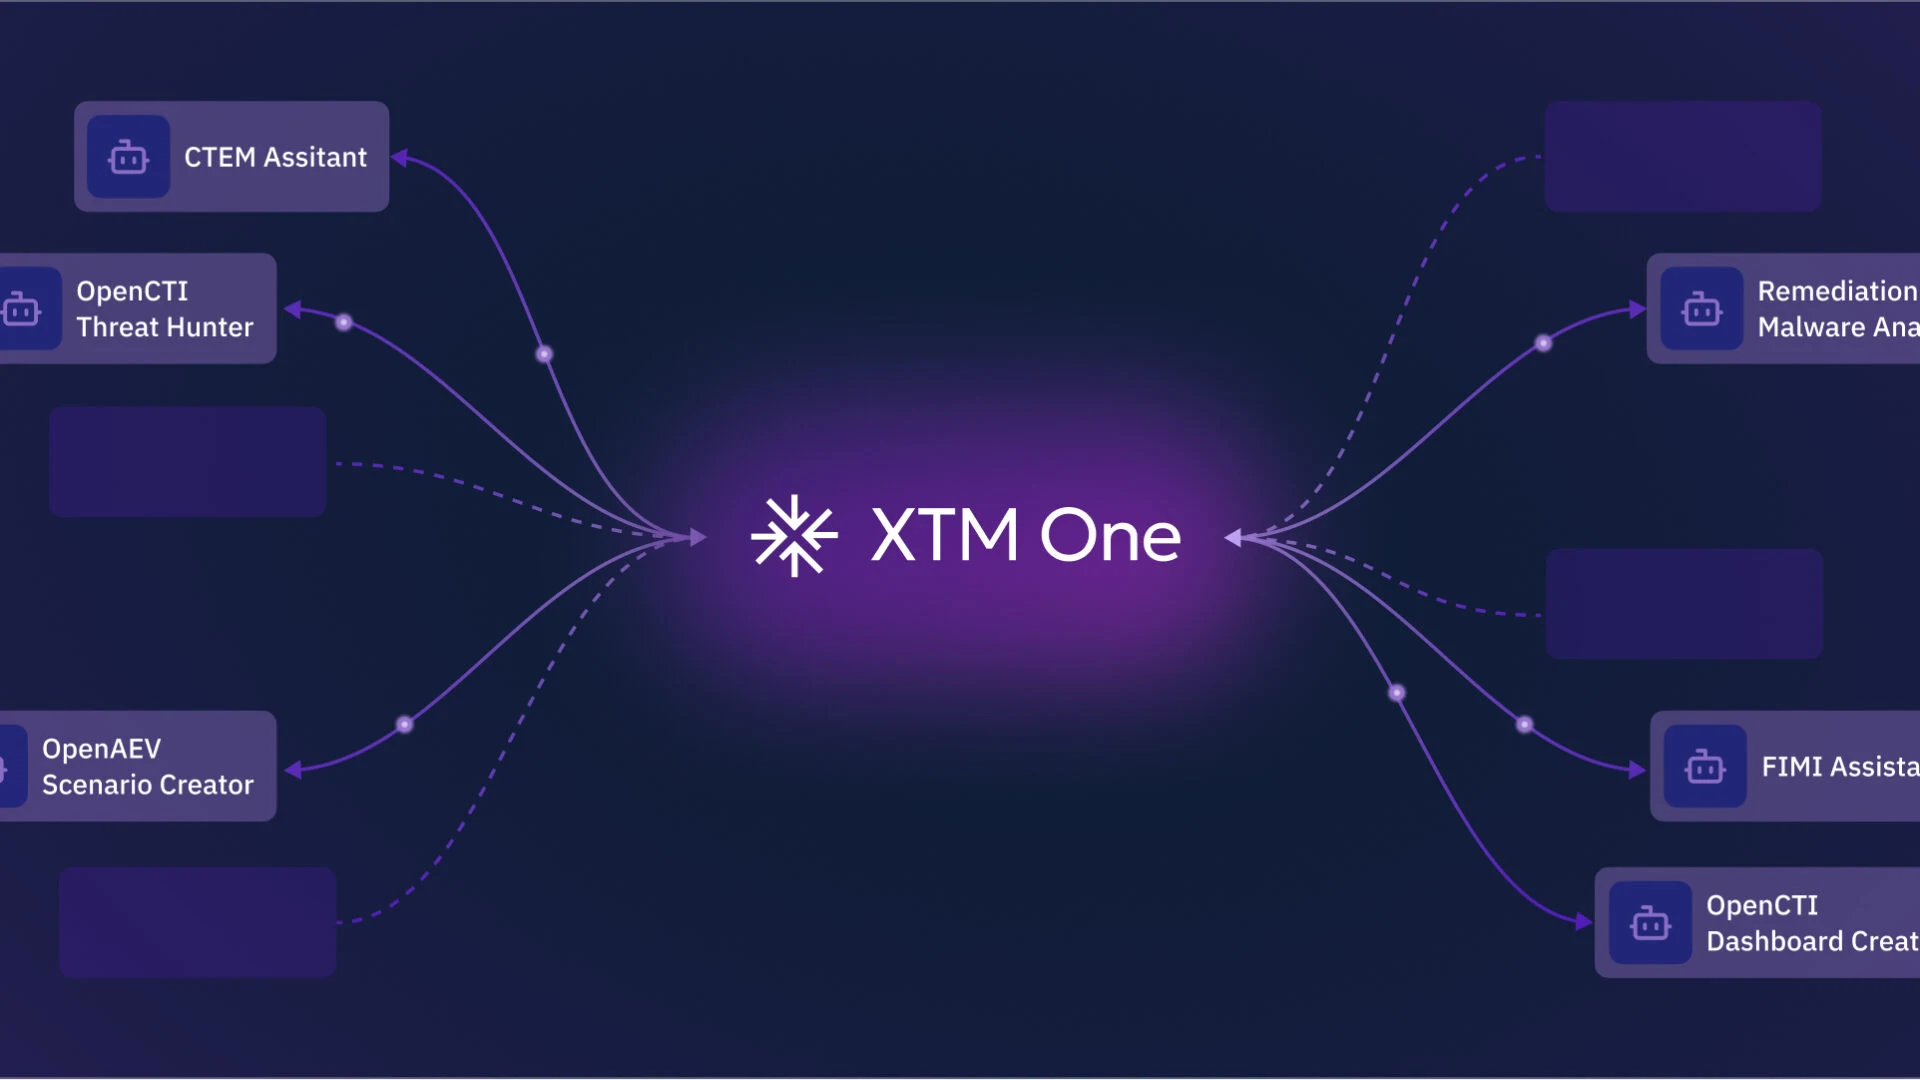
XTM One is the agentic AI layer that consolidates and orchestrates all assistive and agentic AI capabilities
Learn more
Unify threat intelligence, security validation and remediation
Break siloes – address your most exploitable risks.
eXtended Threat Management Platform
Agentic AI Orchestration Layer
XTM One is the agentic AI layer that consolidates and orchestrates all assistive and agentic AI capabilities
Learn more
Cyber Threat Intelligence
Modern security teams are drowning in tools and data
Learn more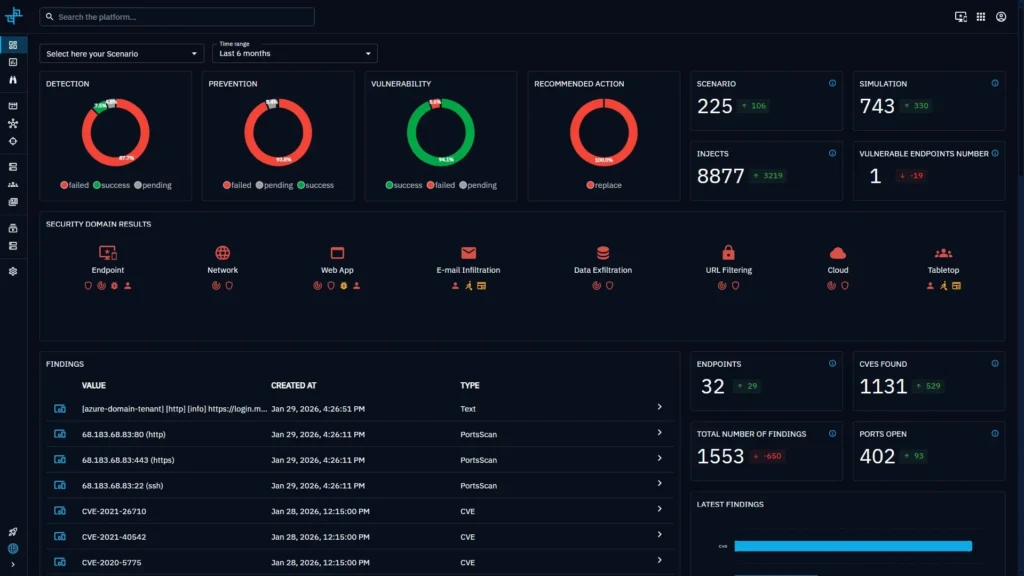
Adversarial Exposure Validation
How confident are you that your security tools will block an attack?
Learn more
Cyber Risk Quantification
transform their static risk compliance assessment into dynamic metrics
XTM One is the agentic AI layer that consolidates and orchestrates all assistive and agentic AI capabilities across the entire XTM platform and supercharges threat-informed exposure management – so you can move from threat signal to validated action at machine speed.
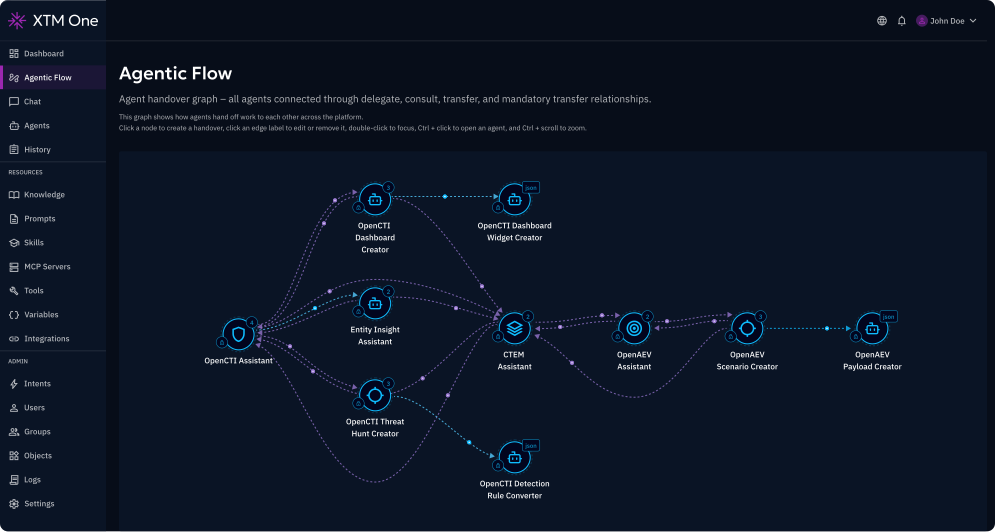
A proactive, threat-informed approach to security where your teams can detect, prioritize, validate and even respond to threats with minimal intervention but with human-in-the-loop to keep you in control of decision making.
Autonomous security operations is no longer a productivity gain, it’s a survival requirement. XTM One is how security teams meet AI-powered threats with AI-powered defense.
50% faster threat hunting and remediation.
Less ramp up time, more expert output – reduce knowledge gaps in the team and deliver consistent, senior level output from day 01 – across OpenCTI and OpenAEV.
70% faster threat detection and response.
XTM One is a programmable orchestration layer, not a closed system. It fits your AI strategy & planning, not the other way around.
Build your own agents, bring your own LLMs.
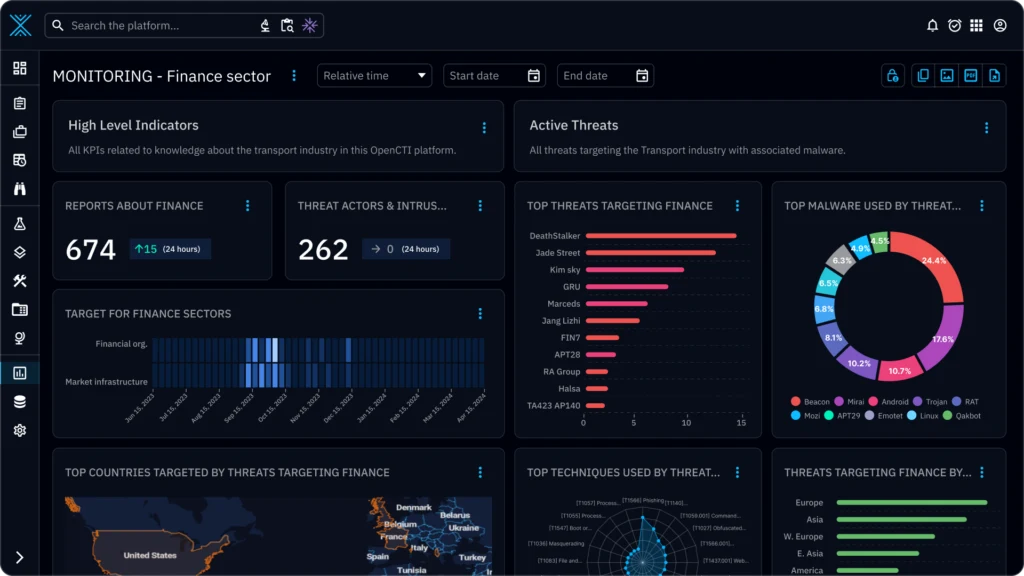
Unify, operationalize and prioritize threat intelligence to make your SecOps better with our open-source threat intelligence platform – the intelligence pillar of CTEM and threat-informed defense.
Operationalize threat intelligence like never before. Share it timely across your security teams and build threat-informed defense.
Standardize all your threat intelligence, from commercial feeds, open source, industry groups or internal security tools, using a consistent STIX 2.1 data model, powerful visualizations and custom dashboards.
Benefit from advanced automation and agentic AI for faster processing of the entire threat management life cycle so you focus on activities that matter. Generate finished TI reports in minutes, not hours or days.
Share prioritized intelligence with your executives to take informed decisions. Feed it into your SecOps for improved detection and response. Scale your threat hunting capacity and validate your security posture, continuously.
Use OpenCTI case management for incident-related data and accelerate your investigations, including threat hunting. Improve your triage, containment and remediation capabilities.
Prove your resilience with real attack simulation, autonomous pentesting, and tabletop exercises with open-source, CTI-driven Adversarial Exposure Validation.
Continuously assess, prioritize, validate and remediate exposures across your attack surface – at both human and technical levels – with open-source, threat-led, agentic Adversarial Exposure Validation (AEV).
CTI-driven BAS mapped to MITRE ATT&CK and ATLAS turns generic scenario libraries into a simulation program built around the threats actually targeting your environment — not a shelf of unrelated techniques.
Agent-orchestrated attack path validation chains techniques the way a real adversary would — full pentesting and red team exercises, executed autonomously, without the cost or scheduling friction of a manual engagement.
Technical controls are only half the picture. Run team-based simulations and social engineering scenarios to pressure-test how your people, escalation paths, and processes actually hold up when it counts.
Continuously fire real-world attack scenarios at your SIEM, EDR, and SOC playbooks. Close the offense/defense loop and turn every simulation into a concrete, actionable detection or response improvement.
Integrations and tech alliances
Here are the general principles we abide by when it comes to AI. All Filigran’s AI features can easily be disabled through the admin console.
We don’t collect any user data for training or validation purposes.
The only information collected is through logs for debugging purposes (with 1 month of retention time, only on our SaaS deployment model).
Customers have the ability to deploy the whole solution on-premise, within their own infrastructure, instead of relying on a fully managed SaaS model.
We give the user full power to define how they want their agent to process information, through deep agent customization. They can choose which models to use, including their own models if they have them, as well as the models we provide.
Explore our wide range of cutting-edge technologies.