
Zero Trust solutions for AI, Endpoints, Cloud, and Network
Allow what you need. Block everything else by default, including ransomware and rogue AI.
Streamlining the way IT professionals handle their cybersecurity, while preventing ransomware
The Platform that Prevents Ransomware
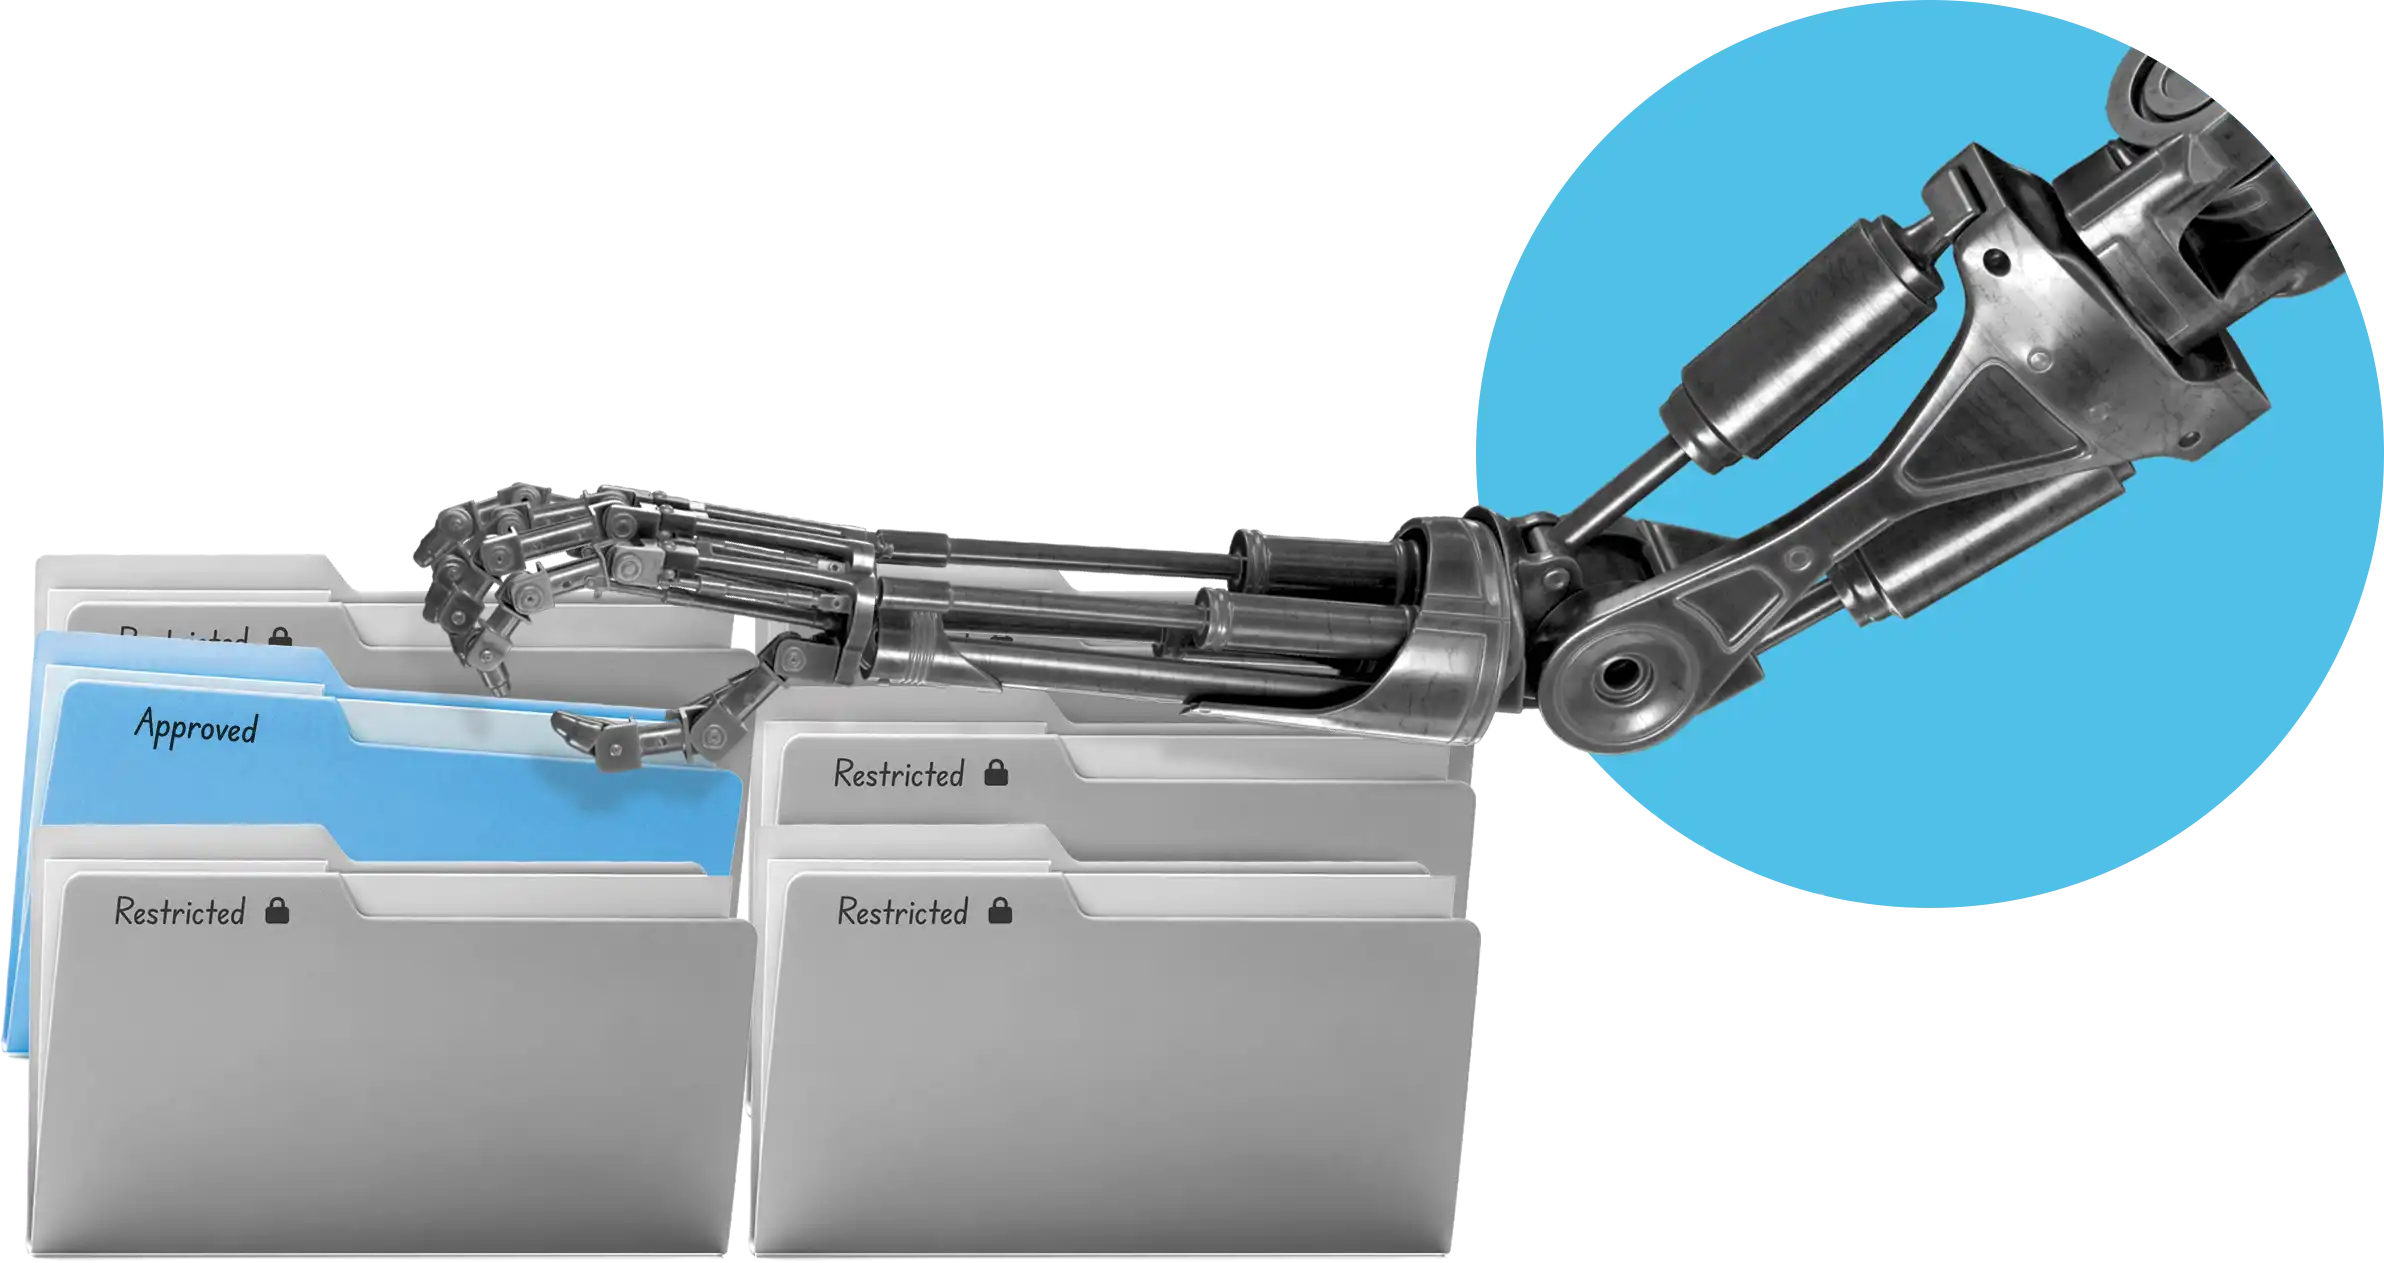
Define exactly how far AI can go
ThreatLocker Zero Trust AI Control (ZTAIC) lets you put AI agents to work without giving up control of your environment. Give agents the access they need to do their jobs while keeping everything else out of reach, even as they invoke other applications and processes.
Stay in charge with comprehensive controls

Zero Trust Network Access
Protect every connection with Zero Trust Network Access.

Zero Trust Cloud Access
Secure your cloud access even when credentials are compromised.

Allowlisting
Take control of what runs in your environment.

Ringfencing
Decide exactly what every application is allowed to do.

External Storage Device
Gain total control over external storage device access.

Data Storage Access Control
Stop data exfiltration before it starts.

Centralized Configuration Management
Set your security standards everywhere.

Privileged Access Management
Remove excessive admin privileges and instantly reduce the risks of a breach.

EDR Real-time Threat Detection
Automatically isolate compromised machines and protect your data in real time.

Managed Detection and Response (MDR)
A full-time Cyber Hero Team on your side, acting in minutes, 24/7/365.

Controlled Application Testing
See exactly what an application will do before it touches your network.

Patch Management
Swiftly remove patching gaps so they don’t become breaches.

Web Content Control
Stop phishing at the browser without adding another security tool.

DAC (Defense Against Configurations)
Turn configurations gaps into strong compliance posture.

Zero Trust Endpoint Firewall
Strictly control device access from anywhere in the world.
Block the pathways attackers try to use
Stop ransomware
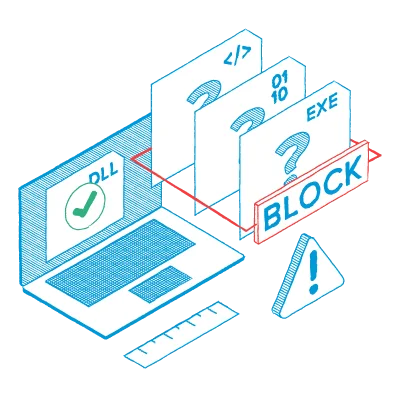
Deny-by-default is your fastest way to break ransomware.
Achieve compliance
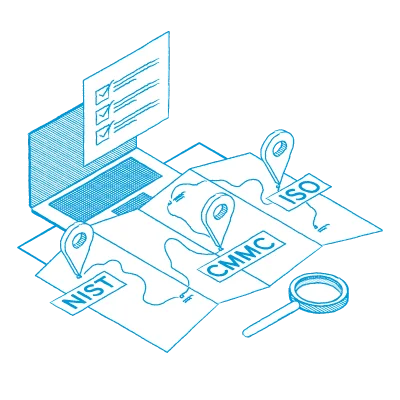
Endpoints are validated continuously, evidence is logged automatically, gaps are flagged, and fixes can be deployed.
Stop token and phishing theft
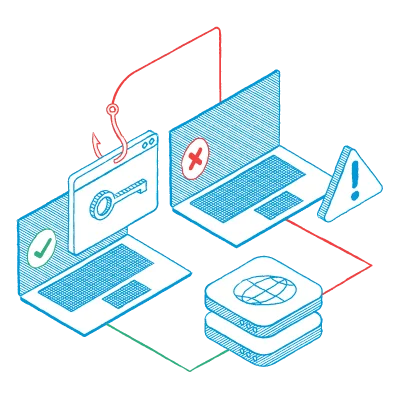
If an attacker logs in from an unrecognized laptop next door or even on the same network, they’re stopped instantly.
Reduce admin privilege abuse
Remove forgotten standing privilege and cut risks immediately.
Stop data exfiltration
Make data exfiltration structurally difficult.
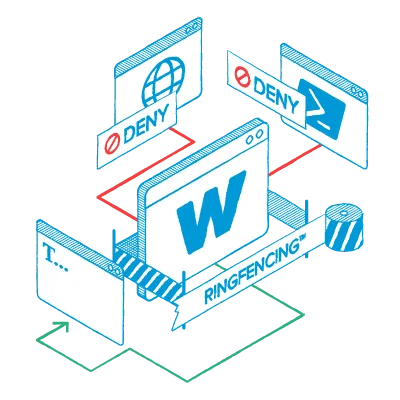
Contain lateral movement
Stop a compromised machine from becoming an enterprise-wide incident.
Why ThreatLocker
Ransomware is malicious software that encrypts files, locking a victim out of their confidential data. If the victim pays the ransom, they may receive a decryption key that will restore their files and data access. If the demanded ransom is not paid, the threat actor may leak their data-on-data leak sites (DLS) such as the dark web and/or permanently block access to their files. As ransomware is distributed by cybercriminals, there is no guarantee that files will be decrypted if the ransom is paid, or that data wasn't immediately leaked onto the dark web.
Application Allowlisting denies all executables, libraries, and scripts from executing, except those that are explicitly permitted to run in an environment.
Many cybercriminals use legitimate encryption tools such as 7-Zip to encrypt files. By using Allowlisting, legitimate tools that have not been explicitly allowed, including those that could be used to encrypt data, are blocked.
The process of deploying Allowlisting is extremely simple. ThreatLocker learns what is required in your environment and, once secured, blocks everything else.
PROACTIVELY PREVENTING THREATS
Solutions Offered
Explore our wide range of cutting-edge technologies.