Secure your Kubernetes workloads. Govern your AI agents.
Migrate VMs to K8s without re-architecting your network.
Kubernetes Networking and Security
One platform for VMs and containers
AI Agent Security for Kubernetes
One control point in the path of every agent call
Products
Secure your Kubernetes workloads. Govern your AI agents.
For Platform Engineering & Security Teams
One platform for VMs and containers
Unified platform for Kubernetes networking and security
The Calico Platform unifies networking, security, and observability across every Kubernetes distribution, on-prem, at the edge, or in the cloud. Bring your VMs to Kubernetes and run them beside your containers through one eBPF-powered management plane.
- No integration tax: one operator installs and manages the full networking and security stack.
- No vendor lock-in: move workloads across distributions and providers on your terms.
- VMs and containers, together: migrate VMs without re-architecting your network.
For AI & Platform Engineering Teams
Your AI agents are making decisions. Do you know what they're authorized to do?
AI Agent Security, Observability & Enforcement for Kubernetes
Lynx gives AI and platform engineering teams complete visibility into agent behavior and authorization controls that govern what agents may do before they act.
- Full visibility everywhere: see what every agent does, accesses, and how it behaves, wherever it runs.
- Authorization before action: Tigera enforces permitted actions automatically and continuously.
- Audit-ready by default: every action, decision, and enforcement event is logged and traceable.
The Solution
One management plane. All your tools. Every environment.
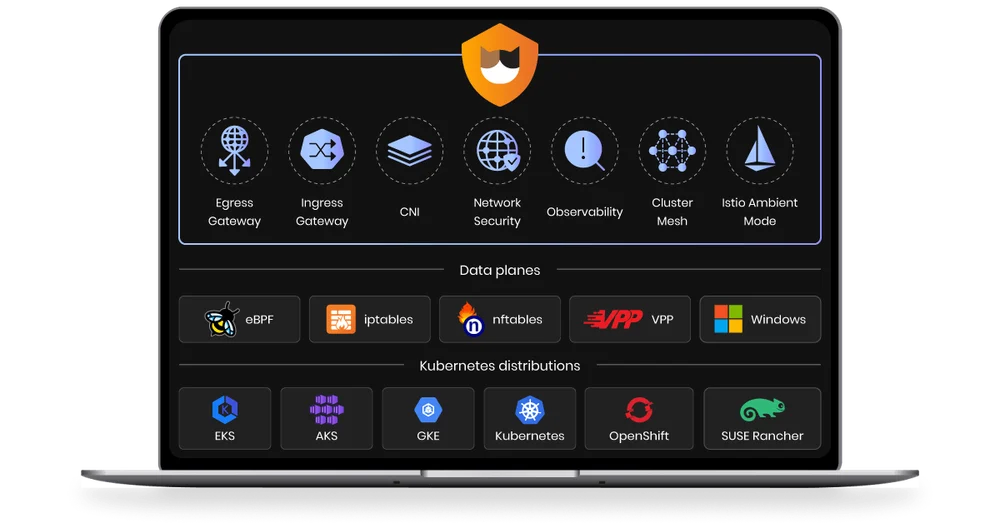
The Calico platform brings Calico Open Source, Istio, and Envoy together under a single operator and a single console — giving your platform team unified control over every type of workload communication without the integration tax.
And because the Calico platform works consistently across every Kubernetes distribution — EKS, GKE, AKS, OpenShift, Rancher, and more — you're never locked into a single provider's ecosystem. Move workloads between distributions freely, on your terms.
Enterprise-Grade Networking, Network Security & Observability
A single platform covering the full spectrum — ingress, egress, pod networking, service mesh, load balancer, VM networking, and multi-cluster networking — combined with enterprise-grade network security controls and deep observability. Everything your environment needs, under one roof.
Unified Management
One operator installs, configures, and manages Calico Open Source, Istio, and Envoy. No stitching tools together. No independent upgrade cycles. No integration gaps.
Distribution Agnostic
The Calico platform works the same way regardless of which Kubernetes distribution you run — EKS, GKE, AKS, OpenShift, Rancher, and more. Your team learns one operational model and it works everywhere, eliminating re-training costs as your infrastructure evolves.
Everything your platform team needs.
Enterprise Networking
The networking foundation for modern Kubernetes environments.
- Pod networking
- Multi-cluster networking
- Service mesh
- Ingress gateway
- Egress gateway
- Load balancer
- VM networking
See what each one does
- Pod networking
- High-performance, scalable pod networking powered by eBPF and Calico Open Source, the most widely deployed CNI in the industry
- Multi-cluster networking
- Seamless connectivity across multiple Kubernetes clusters, enabling distributed applications to communicate securely across cluster boundaries
- Service mesh
- Full-featured service mesh powered by Istio with Ambient Mode — sidecarless mutual TLS, traffic management, and deep observability between services without the resource overhead of per-pod sidecar proxies
- Ingress gateway
- Secure, high-performance ingress traffic management powered by Envoy — controlling how external traffic enters your cluster
- Egress gateway
- Control and secure all traffic leaving your cluster — enforce egress policies, enable NAT, and maintain visibility over external communication
- Load balancer
- Enterprise-grade load balancing for Kubernetes services — distributing traffic efficiently across workloads with full policy control
- VM networking
- All networking capabilities extended to VMs running in Kubernetes — consistent connectivity and policy enforcement across containerized and virtualized workloads
Network Security
The full spectrum of network security, in one platform.
- Network policies
- DNS policies
- Network sets
- Encryption
- Staged policies
- Policy tiers
See what each one does
- Network policies
- Fine-grained, label-based network policy enforcement for Kubernetes workloads
- DNS policies
- Control workload access to external services by domain name, not just IP — a critical capability for dynamic cloud environments where IPs change constantly
- Network sets
- Define and reuse groups of IPs, CIDRs, and domains across multiple policies — reducing policy complexity and maintenance overhead at scale
- Encryption
- Mutual TLS and WireGuard-based encryption for workload-to-workload communication — enforced automatically, without application changes
- Staged policies
- Author and test policies in observation mode before enforcing them — see exactly what traffic would be affected before a single connection is blocked
- Policy tiers
- Define policy enforcement order across platform, security, and application teams — ensuring organizational governance without policy conflicts
Threat Detection
Detect threats. Understand your environment. Respond fast.
- IDS/IPS
- Packet capture
- Dynamic service graph
- WAF (Web Application Firewall)
- DDoS protection
- Alerts
See what each one does
- IDS/IPS
- Intrusion detection and prevention that monitors workload traffic for known threat signatures and anomalous behavior — automatically alerting or blocking based on policy
- Packet capture
- On-demand and policy-triggered packet capture for deep forensic analysis — no external tools required
- Dynamic service graph
- A real-time, visual map of all workload communication in your environment — see exactly how services are connected, what's talking to what, and where anomalies exist
- WAF (Web Application Firewall)
- Protect workloads against common web-based attacks including OWASP Top 10 threats — enforced at the Kubernetes layer without changes to application code
- DDoS protection
- Detect and mitigate volumetric and application-layer DDoS attacks before they impact workload availability
- Alerts
- Configurable alerting on policy violations, anomalous traffic patterns, and threat detections — integrated with your existing SIEM and incident response workflows
Unified Management
Unified Management Plane: One console to rule them all.
- Single operator
- Unified dashboard
- Consistent operational model
- Single pane of glass
- Heterogeneous policy enforcement
See what each one does
- Single operator
- Single operator for installation, configuration, and lifecycle management of Calico Open Source, Istio, and Envoy
- Unified dashboard
- Unified dashboard for visibility across all workload communication types
- Consistent operational model
- Consistent operational model across EKS, GKE, AKS, OpenShift, Rancher, and more
- Single pane of glass
- Single pane of glass for multi-cluster environments
- Heterogeneous policy enforcement
- Policy enforcement extended to VMs and bare metal hosts outside Kubernetes
AI-Powered Policy
Policy Management & Observability
- Policy recommendation engine
- Policy simulation
- Policy hierarchy tiers
- Flow visualization
See what each one does
- Policy recommendation engine
- Automatically evaluates traffic flows and recommends network policies based on observed communication patterns
- Policy simulation
- Test and validate policies in a simulated environment before deploying to production — zero risk, full confidence
- Policy hierarchy tiers
- Define policy enforcement order across multiple teams, ensuring platform and security teams can author policies independently without conflict
- Flow visualization
- See exactly how workloads are communicating, what's being blocked, and what's being allowed — in real time
Multi-Cluster Support
One platform. Every cluster. Every distribution.
- Consistent policy enforcement
- Multi-cluster visibility
- Federated policy management
- Operational consistency
- Support for hybrid environments
See what each one does
- Consistent policy enforcement
- Consistent policy enforcement across every Kubernetes distribution — cloud-managed and self-managed
- Multi-cluster visibility
- Multi-cluster visibility and management from a single console
- Federated policy management
- Author policies once, enforce across multiple clusters
- Operational consistency
- Freedom to move workloads between providers without re-learning operational procedures
- Support for hybrid environments
- Kubernetes clusters, VMs, and bare metal hosts under unified management
Built on the best open-source technologies in Kubernetes networking.
The Calico platform is built on the most proven open-source technologies in the Kubernetes networking and security ecosystem — with a unified management plane that installs, configures, and manages them through a single operator. Best-of-breed capabilities without the integration burden.

Calico
The world's most widely deployed Kubernetes CNI. Chosen freely by millions of developers before it was ever part of an enterprise product.
Istio
The leading open-source service mesh. The Calico platform integrates Istio — including Istio Ambient Mode, a sidecarless architecture that delivers mutual TLS, fine-grained service-to-service authorization, and deep traffic observability without injecting a sidecar proxy into every pod.
Envoy
The high-performance proxy powering Istio's data plane. The Calico platform manages Envoy configuration through a unified control model — delivering advanced traffic management, load balancing, and observability without independent Envoy expertise required.

eBPF
The kernel-level technology that powers high-performance networking and observability. eBPF enables deep packet inspection, network policy enforcement, and real-time flow visibility with minimal overhead — without kernel modifications
All four technologies are open-source with active CNCF communities. The Calico platform gives you enterprise management and support for these tools — without locking you into proprietary alternatives.
Calico Open Source
Networking, network security, and observability that works across any Kubernetes distribution
Calico Open Source provides a unified solution for Kubernetes networking, network security, and observability. It works seamlessly across any Kubernetes distribution, ensuring your workloads are truly portable. Beyond containers, Calico extends network security to virtual machines and bare metal servers, offering a single, consistent security policy framework for your entire infrastructure. Trusted and proven in some of the world's largest enterprises and technology environments, Calico is the most widely adopted solution, powering over 1 million clusters globally.

Pluggable data planes: eBPF, nftables, iptables, Windows, and VPP
Any workload, any Kubernetes distro, any deployment environment
Unparalleled scalability & efficient resource utilization
Real-world production hardened
Three ways to run Calico. One consistent experience.
Calico is available in three editions — all built on the same open-source foundation, all delivering the same core networking, security, and observability capabilities. Start with open source and scale into enterprise features as your needs grow, or go straight to the full platform. Choose based on your operational model — not on whether you're “ready.”

Calico Open Source
The foundation. Calico Open Source delivers high-performance pod networking, network policy enforcement, and core networking capabilities — free, open-source, and community-supported. Millions of developers and organizations already run Calico Open Source in production. It's the most widely deployed CNI in the industry, and it's the starting point for everything the Calico platform offers.
- High-performance pod networking with eBPF
- Kubernetes network policy enforcement
- Active open-source community and documentation
- The foundation that Calico Cloud and Calico Enterprise build on".

Calico Cloud
The fastest way to get the full Calico experience. Calico Cloud is a fully managed SaaS offering: Tigera handles the infrastructure, upgrades, and operations so your team can focus on securing workloads, not managing the platform itself. Everything in Calico Open Source, plus unified management, Istio and Envoy integration, and enterprise-grade security and observability.
- Everything in Calico Open Source, plus:
- Unified management plane for Calico Open Source, Istio, and Envoy
- Policy recommendations and troubleshooting
- Enterprise-grade network security, threat detection, and observability
- Fully managed; no infrastructure to operate
- Free trial available; start immediately, no credit card required".

Calico Enterprise
For organizations that require full control over where their data lives and how the platform is operated. Calico Enterprise deploys in your own environment (on-premises, air-gapped, or in your own cloud) with the same full feature set as Calico Cloud, backed by enterprise support and SLAs from Tigera.
- Everything in Calico Cloud, plus:
- Full control over deployment and data residency
- Supports air-gapped and on-premises environments
- Enterprise support and SLAs
- Designed for organizations with strict compliance and data sovereignty requirements".
For Platform Engineering, AI & Security Teams
AI Agent Security for Kubernetes
Your AI agents are making decisions. Do you know what they're authorized to do?
The unified control plane for AI agent discovery, identity, authorization, and runtime enforcement for every agent in your organization running on Kubernetes. Guardrails, not gates.
Unified control across teams
For AI & Platform Engineering Teams
- Deploy agents faster with comprehensive observability
- Runtime enforcement without blocking workflows
- Identity and authentication for every agent
For Security Leaders
- Complete visibility into every agent; shadow agents too
- Zero-trust authorization enforced before every action
- Full audit trail for compliance and incident response
Everything you need to govern AI agents at enterprise scale.
Discovery, Registration & Observability
Know every agent in your estate, registered or shadow
Central Registry
A directory of every agent with owner, purpose, version, context. Full APIs for CI/CD registration at deploy time.
eBPF Auto-Discovery
Find every agent running, including ones nobody registered. Detected by behavior (library loads, MCP traffic, TLS SNI).
Shadow Agent Detection
Discovered agents are cross-referenced against the registry.
Observability
Reconstruct any agent's actions end-to-end: what it saw, what it decided, which tools it called. Open Telemetry traces.
Configuration & Posture Management
Fine-grained authorization for every agent interaction before it happens.
Continuous Posture Assessment
Continuously evaluate every registered agent's configuration against security baselines. Detect drift the moment it occurs — not at the next scheduled scan. Surface over-permissioned tools, excessive scopes, missing identity bindings, and exposed MCP servers before they become incidents.
Sandbox Environments
Provide a sandbox environment for each agent with a controlled blast radius. Leverage eBPF to control kernel primitives applied to the cluster before any agent runs. Customer-configurable baselines for safe operation by default.
K8s-Derived Context
Posture policies derived from actual K8s configuration — namespace, service account, RBAC bindings, and network policy — not just agent metadata.
Compliance Baselines
Pre-built policy packs for common compliance frameworks. Map agent configuration gaps directly to GDPR, HIPAA, SOC 2, and financial services requirements.
Agent Identity & Authentication
Every agent needs a verified identity. Not a shared API key.
SPIFFE/SPIRE SVIDs
Cryptographic workload identities issued to every agent. Integrates with Microsoft EntraID, Okta, and existing IdPs. Private key never leaves the workload.
No Shared Secrets
Eliminates long-lived API keys entirely. Short-lived tokens with ~10-minute TTL are automatically rotated. Credential theft becomes operationally useless.
Chain of Custody
Tracks On-Behalf-Of delegation chains via RFC 8693 token exchange. Every hop in a multi-agent workflow is cryptographically attributed.
Token Exchange at Gateway
Standard Mode replaces caller tokens with gateway-minted JWTs. Passthrough Mode preserves the original token for downstream verification alongside the gateway JWT.
Policy Definition & Enforcement
Guardrails, not gates. Enforcement that doesn't slow your AI & platform engineering teams down.
Runtime Enforcement
Istio Ambient Mesh: ztunnel at L4, waypoint proxy at L7. Every policy evaluated in real-time before any action. Break-glass quarantine. HIL hooks.
Tool Binding
Restrict exactly which LLM, MCP server, API endpoint, or tool an agent can access. Bindings enforced at the gateway — not in agent code.
Describe Policy in Natural Language
LLM-assisted authoring of Cedar policies. Plain English expression of desired intent. Lowers the cognitive burden on authoring policies.
Anomalous Behavior
See everything. Trace every action. Prove it to the auditor.
Behavioral Anomaly Detection
eBPF empirical classifier and behavioral baseline built from real agent traces. Detects anomalies — credential theft, lateral movement, supply-chain compromise — that static signatures miss.
Forensic Audit Trail
Full reproducible audit trail satisfies GDPR, HIPAA, SOC 2, and financial services requirements. Every agent decision is logged with cryptographic attribution.
eBPF & LSM to Watch Agent Behavior
Leverage eBPF & LSM to watch agent behavior on a continual basis and feed traces to the anomaly detection engine. Use Cedar policies to configure eBPF & LSM controls per agent. LLM-assisted authoring of Cedar policies.
Red Team Agent
LLM-driven adversarial agent continuously probes the cluster for posture gaps — IAM misconfigs, over-permissioned tools, exposed MCP servers — before attackers do.
Know every agent before they do something they shouldn't.
One security and governance standard.
Lynx meets you where your agents are.
Self-hosted
Lynx is a Kubernetes-native gateway deployed in your cluster, sitting in the middle of all agentic traffic and enforcing policy at runtime. Control and data plane fully managed by you.
Ideal for: Kubernetes-native agent deployments requiring full control over data residency.
Ready to see everything and control everything?
Whether you're securing Kubernetes workloads or governing AI agents, Tigera gives you the control and visibility to run mission-critical environments at scale.
Solutions Offered
Explore our wide range of cutting-edge technologies.